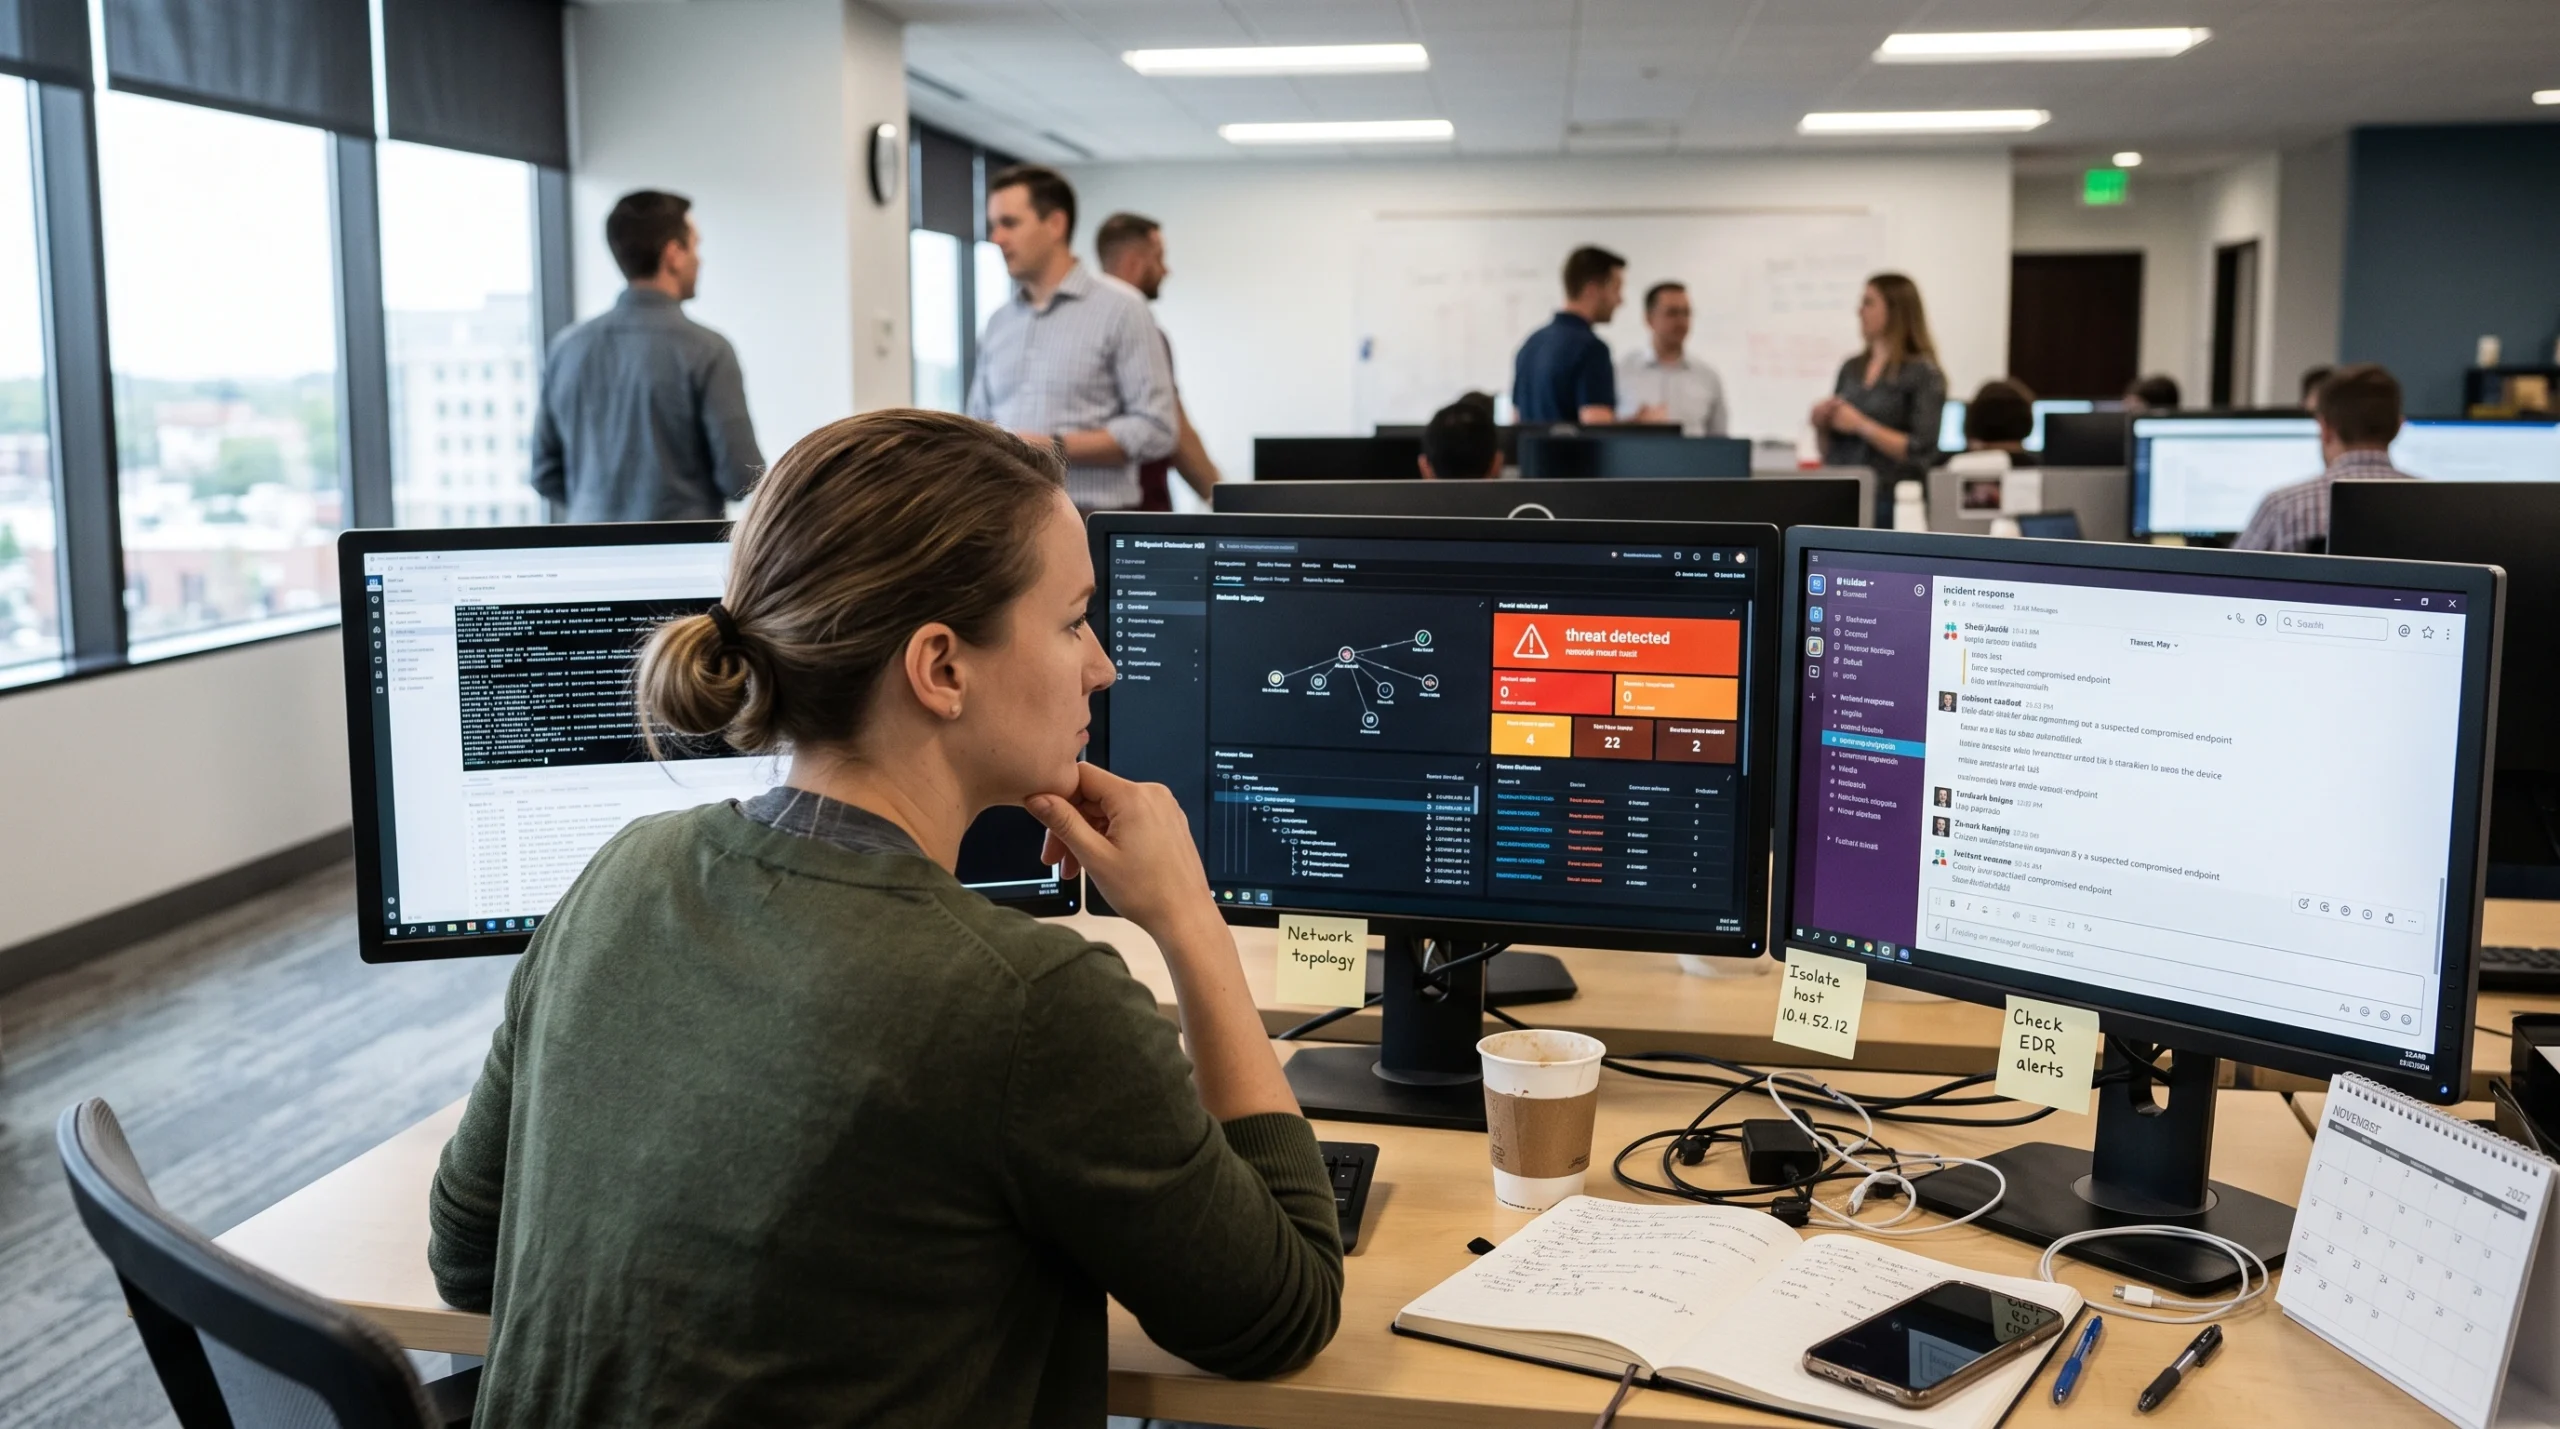
Most data breaches don’t start on a server. They start on a laptop that went home years ago and was never checked again, or a phone that logs into email but was never enrolled in anything. That’s the quiet story behind most unmanaged device security risks: nothing dramatic happens until the one device nobody was watching becomes the way in.
What Counts as an Unmanaged Device
An unmanaged device is any endpoint that connects to company systems without being enrolled in a management or security platform. That includes personal phones and laptops used for work, contractor equipment, devices left behind by employees who no longer work there, and smart devices sitting quietly on the office network.
None of these are unusual. Most organizations have some version of all four. The issue isn’t that they exist. It’s that nobody has a current, accurate list of them, and that gap in device visibility is where risk quietly builds.
Are Personal Devices a Security Risk for Your Business?
Yes, and not because employees are careless. A personal phone used to check email or a laptop used to log in to a shared drive was never designed with the company security policy in mind. It has whatever settings the owner chose, whatever apps they installed, and whatever protection they happened to turn on, or didn’t.
This is the core of most BYOD security risks: the device itself isn’t the threat. The absence of any standard around it is.
Why This Blind Spot Keeps Growing
Remote and hybrid work made personal devices a normal part of how people get things done. A contractor needs temporary access. An employee checks email from their own phone. Someone leaves the company, and the laptop they were issued sits in a drawer, still technically able to connect.
Each of these is a small, reasonable decision on its own. Together, they create a surface that grows faster than most IT processes are built to track. The result isn’t a single bad decision. It’s an accumulation of normal ones that nobody consolidated.
The Gap Between Knowing a Device Exists and Knowing How Exposed It Is
Knowing a device is on the network is not the same as knowing its condition. Is it encrypted? Has it been patched? Does it have any protection installed at all?
A 2025 device security report analyzing over 27 million connected devices across more than 1,800 enterprise networks found that nearly a third of devices on corporate networks operate outside IT’s control, and nearly four in ten company-owned devices registered in the organization’s directory don’t have active endpoint protection. In both cases, the device shows up somewhere. What’s missing is an accurate read on its actual exposure, not just its presence.
What Percentage of Data Breaches Start With an Unmanaged Device?
This isn’t a theoretical concern. A Verizon 2025 Data Breach Investigations Report examined cases where corporate credentials appeared in infostealer logs and found that nearly half of the devices associated with those compromised credentials were never enrolled in any company security tool.
The pattern holds across multiple studies: attackers don’t need to break through a well-defended system when there’s an unmonitored one sitting right next to it.
What Is the Difference Between MDM and EDR?
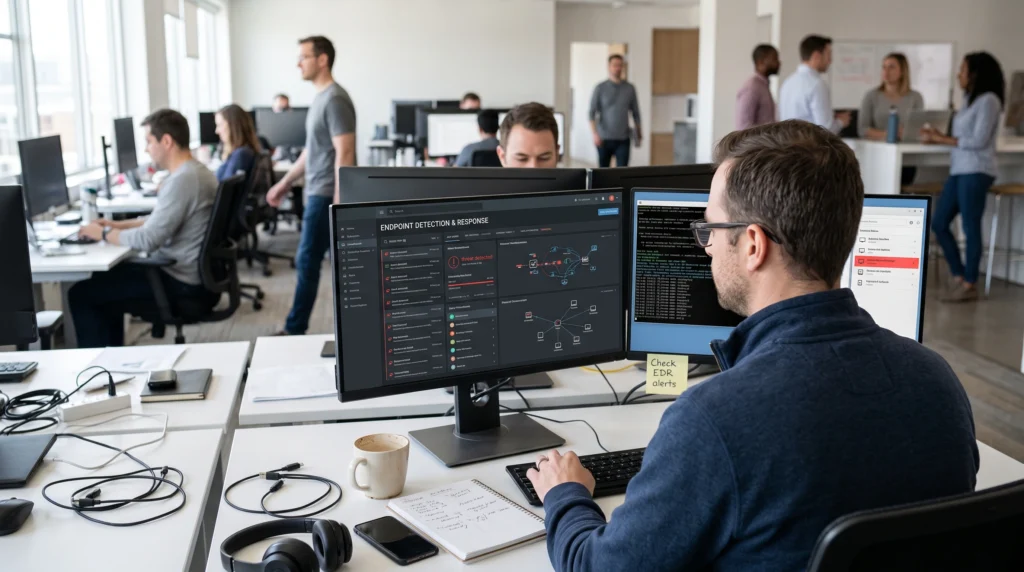
The two get used interchangeably, but they solve different problems. Mobile device management, or MDM, is about managing a device: enforcing settings, pushing updates, controlling what’s installed. Endpoint detection and response, or EDR, is about watching behavior on that device and responding when something looks wrong, even when the specific threat has never been seen before.
A well-managed device isn’t automatically a monitored one, and a monitored device isn’t automatically configured correctly. Reducing unmanaged device security risks usually means having both, not choosing between them.
Visibility, Detection, and Lifecycle: The Layers That Actually Matter
Beyond MDM and EDR individually, closing this gap comes down to three things working together, not one tool solving everything.
Visibility and inventory. You can’t protect a device you don’t know exists. An accurate, current inventory is the starting point for everything else.
Detection and response. Once a device is known, it needs ongoing monitoring, not a one-time check.
Encryption and lifecycle management. A device that leaves the company, whether through an employee’s departure or hardware replacement, requires a defined process for wiping, decommissioning, or retiring it. Otherwise, it remains a live risk long after anyone is thinking about it.
Do You Need EDR If You Already Have Antivirus?
Traditional antivirus looks for known threats, files, and patterns that have already been identified elsewhere. That approach still catches plenty, but it struggles against anything new or slightly modified. EDR closes that gap by monitoring for suspicious behavior rather than only matching known files.
For a device that isn’t centrally managed, that difference matters more, not less, because there are fewer other safeguards around it.
How to Reduce BYOD Risk
None of this requires banning personal devices or slowing people down. A few principles cover most of the ground:
- Keep an inventory that reflects reality, not just what the company issued.
- Require encryption on anything that touches company data, personal or not.
- Define what happens to a device the moment someone leaves, before it becomes an afterthought.
- Treat detection as a baseline for any device with access, not a bonus for company-owned equipment only.
None of these are complicated on their own. What’s usually missing is someone accountable for making sure they happen consistently.
When a Missing Device Becomes a Compliance Problem
In organizations that handle sensitive client, patient, or financial information, a lost or unaccounted-for device isn’t only a technical loose end. It can become a reporting obligation, a client conversation, or a regulatory question, depending on what was on it and whether it was encrypted.
That shift, from a lost laptop to an obligation to explain what was on it, is usually what turns a quiet gap in visibility into a very public problem.
Talk to Someone Before an Incident Forces the Conversation
Reducing unmanaged device security risks doesn’t start with predicting every possible attack. It starts with an honest answer to a simpler question: does anyone currently have a complete, accurate list of every device touching your systems, and do you know the condition of each one?
If that answer isn’t a confident yes, talk to our team about a quick device visibility review before an incident forces the answer instead.

NetVoiX ayuda a las empresas a maximizar sus inversiones en tecnología proporcionándoles servicios informáticos completos, puntuales y rentables.
SOLUCIONES TECNOLÓGICAS IMPULSADAS POR NUESTROS VALORES